

The steps below are for macOS. On Windows, the Codex policy works as it does on macOS, and provider lockdown isn’t available, though you can record that a secure web gateway already blocks the provider APIs; see Install on Windows.
Provider lockdown
Provider lockdown is one switch, set when you render the MDM profiles. With it on:- Direct LLM provider APIs are blocked, so traffic can’t skip the gateway:
api.anthropic.com,api.openai.com, Gemini, Vertex AI, Bedrock runtime, Azure OpenAI and AI Services, Mistral, Groq, Together, OpenRouter, DeepSeek, xAI, Cohere, Perplexity, Hugging Face inference, Fireworks, Cerebras, and Replicate, plus the public DNS-over-HTTPS resolvers that would get around the block. The providers’ sign-in hosts (claude.ai,console.anthropic.com,auth.openai.com), Barndoor’s hosts, and your gateway stay reachable. - Claude runs only through Barndoor. The updater installs the Claude policy (Claude Code managed settings plus a fallback Claude Desktop profile). A
claudestarted from a terminal has every prompt refused with a message pointing atbarndoor run claudeand the Bridge app, and Claude Desktop opened directly shows a profile named Barndoor (open Claude Desktop from Bridge) that can’t reach Claude.
chatgpt.com and gemini.google.com, in a browser: DNS can’t tell those apart from the sign-in flows Bridge needs.
Pick one of two ways to block the provider APIs:
Either way, the next run of
install-latest.sh installs the Claude policy and keeps it current. Re-render without lockdown and the next run removes it, along with nothing it didn’t write.
If a Mac already has a
/Library/Application Support/ClaudeCode/managed-settings.json of your own, the updater doesn’t overwrite it and reports a failure instead. Merge the output of barndoor claude-policy print into your file.barndoor doctor. With lockdown on, expect:
present but NOT blocked means lockdown is on but a provider host is still reachable: check the resolver policy or your secure web gateway’s rules.
Codex policy
The Codex policy is Codex’s system requirements file,/etc/codex/requirements.toml. The updater installs it on every managed Mac, whether or not provider lockdown is on, and keeps it current.
With the policy on a Mac:
- Launch Codex Desktop appears in Bridge when Codex Desktop is installed at
/Applications/ChatGPT.app. Without the policy, Bridge shows no button. codexin a terminal, and Codex in the ChatGPT app opened directly, refuse to run outside Barndoor.barndoor run codexand Launch Codex Desktop work. Tell people before you roll it out.
- It replaces a requirements file of your own on every run. If your fleet ships its own Codex requirements, opt out.
- Don’t ship a copy of the file through your MDM. A Bridge release can change the policy, and launches refuse an out-of-date one. Let the updater install it.
- The behaviour is in the script. MDM consoles run the script text you pasted, so a fleet gets the always-on Codex policy only once you paste the current
install-latest.sh. - If one policy fails to install, the updater still installs the others, then exits non-zero so your MDM reports it.
--no-codex-desktop-policy, or set BARNDOOR_MDM_CODEX_DESKTOP_POLICY=0 in its environment. That removes only a file Barndoor wrote, and Launch Codex Desktop is no longer offered.
On a Mac without the policy, barndoor codex-desktop-policy verify says what’s missing:
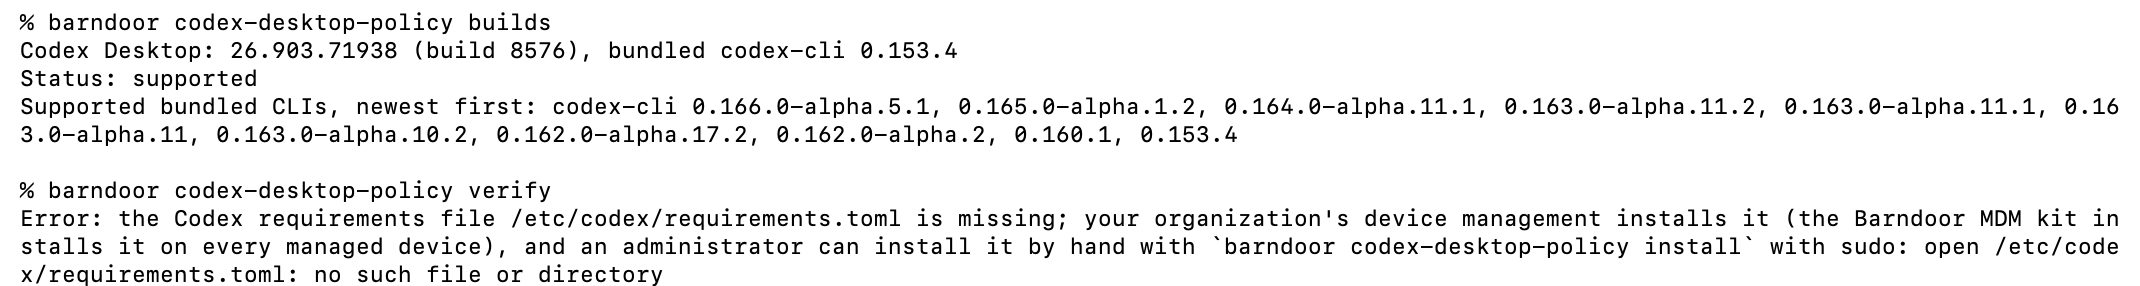
sudo barndoor codex-desktop-policy install and remove it with sudo barndoor codex-desktop-policy remove.
Hold Codex Desktop updates
Codex Desktop updates itself. Barndoor supports the Codex Desktop versions it has reviewed, normally the current one and a few before it, and adds new ones in later Bridge releases. Until then, a Mac that updated early fails to launch with “newer than this Barndoor supports”. To hold Codex Desktop at the version you deploy, render with--hold-codex-desktop-updates and deploy codex-desktop-updates.mobileconfig like the other profiles. It turns off Codex Desktop’s automatic update checks and downloads, with or without provider lockdown.
- It must be a managed profile. Codex Desktop rewrites its own update settings at launch, so
defaults writedoesn’t stick. - Check for Updates… in the ChatGPT menu still works. Where people don’t have administrator rights and the app is owned by root, macOS asks for an administrator password.
- Homebrew can still replace the app.
brew upgrade --greedy, orbrew upgrade --cask chatgpt, installs a new ChatGPT.app regardless. Leavechatgptout of greedy upgrades on these Macs.
barndoor codex-desktop-policy builds. Once it reports Status: supported, deploy that version to the fleet. The command exits non-zero only when a launch would refuse the installed version, so it also works as an MDM audit. To stop holding updates, remove the profile.
Claude Desktop managed profile
With the Claude policy, Claude Desktop opened directly gets a fallback profile that can’t reach a model. That profile is a file people can edit or delete, though the next updater run puts it back. To make it tamper-proof, deploy Claude Desktop’s Barndoor configuration as a managed profile instead. People then can’t change where Claude Desktop sends requests or which MCP servers it has, or switch it to a personal claude.ai account.- Render with
--claude-desktop-managed <capabilities.json>, a file with the capabilities Claude Desktop gets on every Mac in the group.render.shuses the Barndoor CLI on the rendering Mac to produceclaude-desktop.mobileconfig, and turns the setting on in the managed settings profile. - Deploy both
claude-desktop.mobileconfigand the new managed settings profile to the same devices, at device scope. - On a Mac,
barndoor doctorreportsClaude Desktop managed profile: ok.
- Deploy and remove the two profiles together. If a Mac has only one of them, Bridge refuses to launch Claude Desktop, and
barndoor doctorreports aDISAGREEMENT:ormissingline. - The profile is a ceiling. If someone’s client settings allow more than the profile, the launch runs limited by the profile. If their client settings are stricter than the profile, the launch is refused, because Claude Desktop’s chat and Cowork can’t be narrowed per session.
- One governed Claude Desktop per Mac, on a fixed local port (47566 unless you render with
--claude-desktop-port). - Claude Desktop applies a changed profile when it relaunches, which it forces within 24 hours.
- Roll it out to a small group first, as with any profile that changes how Claude Desktop starts.
Santa rules
The MDM kit includes optional Santa rules insanta/ that block unapproved AI desktop apps, such as Cursor and the ChatGPT chat app, while allowing Barndoor, Claude, and Codex. Deploy the monitor rules first, then switch to the deny rules once you’ve seen what they would block. The kit’s guides/ folder covers delivery for each MDM.